At a glance#
The Workstation runs agents on your computer or a connected host. Your chosen AI provider processes their requests under your provider account. Connecting that computer to a Halofy team also starts sharing with your teams and their authorized managers:
- New conversations: supported user and assistant text, tool inputs and results, and available helper-agent conversations.
- Current-month usage: numeric usage and model/provider identifiers, including available usage from earlier this month. Earlier conversation text is not backfilled.
- Supported plan details: detected subscription or API-key status; not provider credentials or account emails.
- Setup for playbooks: supported authored instructions, skill text and safe settings from registered projects and supported agent profiles, collected when requested.
File and image attachments are excluded from conversation capture, but tool results can contain text read from files. Setup collection can contain private authored instructions. Read the sections below before connecting. Signing out stops sharing; there is no separate pause switch.
What stays on your computer#
Halofy runs each provider's agent on your computer, or on another computer you connect to. Your threads, projects and the files you attach are stored on the computer that runs them. A few providers, such as Grok Bot, work on the provider's own remote computer instead.
- Provider logins stay in each provider's own storage on that computer. Removing a provider in Halofy removes Halofy's connection, not the provider's credentials on disk.
- API keys you enter for a provider, such as DeepSeek, are stored as secrets for that provider connection. Commands Halofy shows you never include stored secrets.
- The desktop app encrypts saved credentials for connections to your other computers with your operating system's secure storage. On macOS this is the Keychain item Halofy Safe Storage. If secure storage isn't available, those credentials aren't saved.
- Output from provider sign-in is kept in memory, not saved as terminal history. Provider tools may keep their own login logs.
- Your Halofy account sign-in is saved on the computer that runs Halofy.
What your AI providers receive#
When you send a message, the provider's agent processes it with your account, just as it would in that provider's own tool. That includes the files and command output the agent reads while it works. Your account with that provider governs this processing, and usage limits and billing stay with the provider.
Halofy adds some context of its own. Brief instructions about Halofy features go to the agent with your messages, and in a team conversation, the team's instructions, policies and any skills the agent reads become part of what the provider receives.
Your Halofy account and team configuration#
Signing in links your devices. Connecting this computer to a team also starts the disclosed sharing of chats, usage and setup. Read the sign-in disclosure before proceeding.
Halofy reads the current team configuration for team conversations. It does not overwrite your project’s instruction files. Provider credentials stay on the host computer.
Account-based device traffic passes through Halofy’s connection service. It is encrypted in transit, but not end to end: the service can process the traffic it forwards. For a direct connection, pair over your local or private network. See remote access.
Team activity: what's shared and when#
Connecting this computer to your Halofy team automatically shares new conversations, this month’s AI usage (including available usage from earlier this month), supported plan details and project setup for playbooks. The sign-in and team-selection screens explain this sharing with your teams and their authorized managers.
There is no separate activity opt-in or pause switch. Team activity shows sharing status. Signing out stops sharing; reconnecting resumes it automatically.
Read what is included and excluded before connecting a computer. Live teammate control is a separate Collaboration setting.
Capture includes supported new conversations started locally or from paired devices, available helper conversations, tool inputs, results and failures, and reported usage. Tool content can include commands, file paths and text read from files. Coverage varies by provider.
File and image attachments, imported histories and earlier conversation text are not backfilled. Large or unsupported payloads can be represented by fingerprints instead of their original content. Numeric current-month usage is a separate feed and may include earlier usage; this does not upload the corresponding old chat text.
Conversations are attributed to the signed-in host account. Review the sharing disclosure on that computer, including when using paired devices. Authorized managers can access captured content under the workspace’s retention and erasure rules.
Last acknowledged upload means delivery was confirmed. On or a successful sign-in alone does not prove that all chats have uploaded. Pending content is encrypted on the host. Queued batches expire from retry after seven days; cleanup occurs when the queue is next accessed. A stopped computer cannot perform that cleanup.
If status says Needs attention, use Retry connection and read the account or team error. Signing out or changing teams stops the current sharing connection; reconnecting resumes it. Previous queues remain tied to their original recipient. Start a new conversation after reconnecting: chats open while sharing was stopped remain excluded.
Agents connected from the Console#
Agents you connect from Agent connections with the installer command can also send supported conversation activity. Your activity may be retained for your authorized managers to review. Before connecting, review the installer’s capture details and type CONNECT to confirm before any changes are made.
In the Console#
- Sign-in. You sign in with Google, GitHub or email, depending on what the sign-in page offers. In Settings, you can connect or disconnect sign-in methods, as long as one stays connected.
- Access. Captured conversations are stored encrypted, and roles decide who can read them: the person a session belongs to, the organization's owner, and the admins who manage that team.
- Summaries. The Console creates a short summary of each captured session. Summaries appear in Sessions and in exports.
- Credentials. API keys you add in AI models are write-only. The Console shows Encrypted and stored, never the key itself.
- Assistant. Questions you ask the Assistant are answered by a model your workspace deployed in AI models, using only information you're allowed to see.
- Audit. Audit records every read, write, deletion and export of your organization's memory. See Audit log.
Retention, erasure and export#
Retention applies to all captured conversations in your organization. You'll find these controls in a connection's details under Agent Connections, and on the Export page.
| Control | What it does | Who can use it |
|---|---|---|
| Keep conversations | Sets how long captured conversations are kept: 30, 90, 180, 365 or 730 days, or Indefinite. Unless changed, conversations are kept for 365 days. Each session shows its Kept until date. | Owner |
| Place legal hold | Stops a session from being deleted when its retention period ends. Release legal hold applies the retention period again. | Owner |
| Erase | Permanently removes a captured session and its attributable derivatives. A reason code is required, and it can't be undone. | Owner, admin |
| Export | Downloads session details and summaries for the organization, a team or a person. A stated purpose is required and each export is recorded in the audit log. Raw messages and tool calls aren't included, and erased sessions never are. | Owner, admin |
Product usage data#
Separately from team activity, the Workstation sends product usage events that help Halofy understand how the app is used. Examples are the app starting, a thread being created, and an agent session starting or a turn finishing.
Events carry details such as the provider, model, permission mode, token counts, durations and counts of projects and threads, along with the app version, operating system and processor type. They're sent with a hashed identifier, not your name or email address, and they don't include your prompts, replies, file contents or file paths.
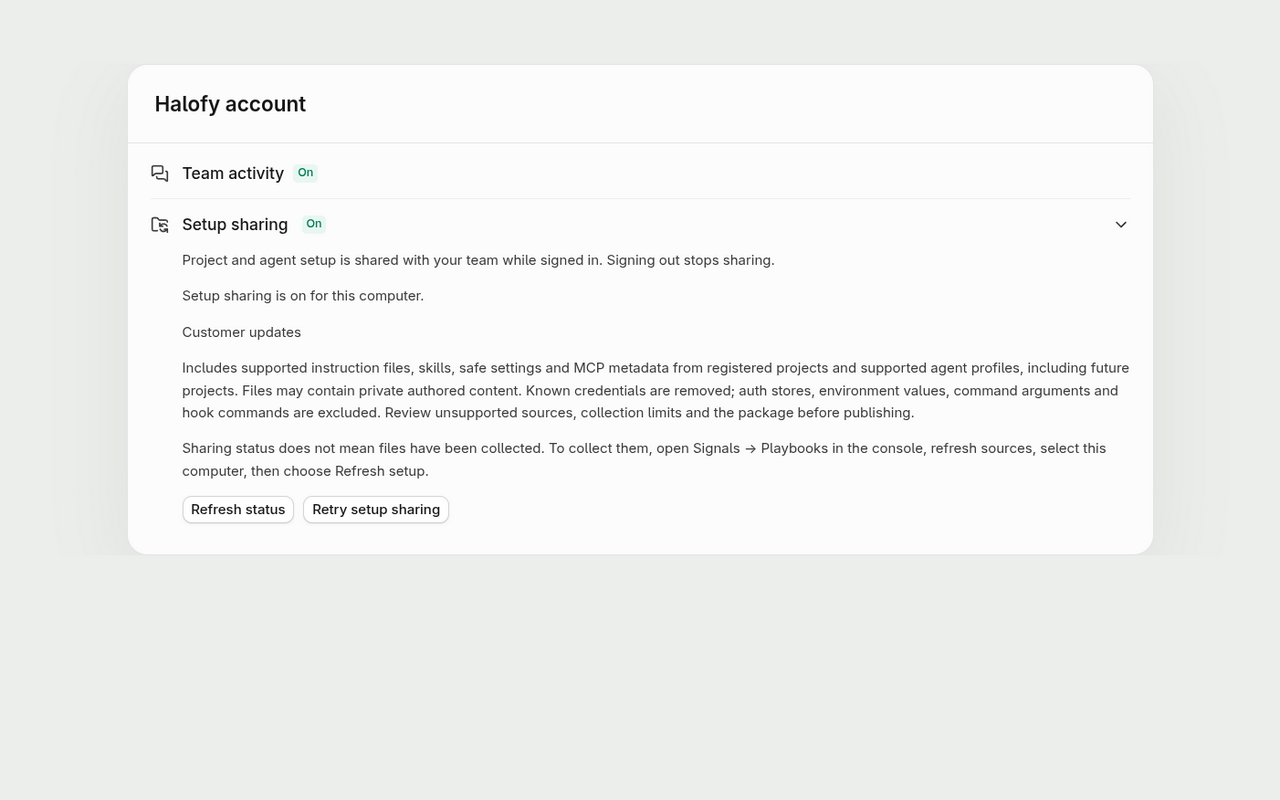
Current setup sharing is separate from chat sharing#
Connecting a computer to your team also registers a setup for playbooks. Setup sharing concerns written instructions and settings; conversation sharing concerns what you and the agent say and do. The current sign-in disclosure covers both, alongside numeric usage and supported plan details.
An authorized setup request can collect supported instruction documents, skill text and safe settings from every registered project on that computer, including projects added later, and supported default agent profiles. This can include the contents of your written project instructions. Unregistered folders are not scanned for this feature.
Collectors remove known credentials and exclude credential stores, environment and header values, executable arguments and hook commands. Missing, linked, unsupported or omitted material stays visible for review. Review the resulting package before publishing it; it is a current snapshot, not proof of what a previous conversation used.
Inspect Setup sharing in Halofy account settings. Signing out stops sharing; reconnecting can register it again. There is no separate setup-sharing toggle. See setup status and refresh.
Protected text and private responses#
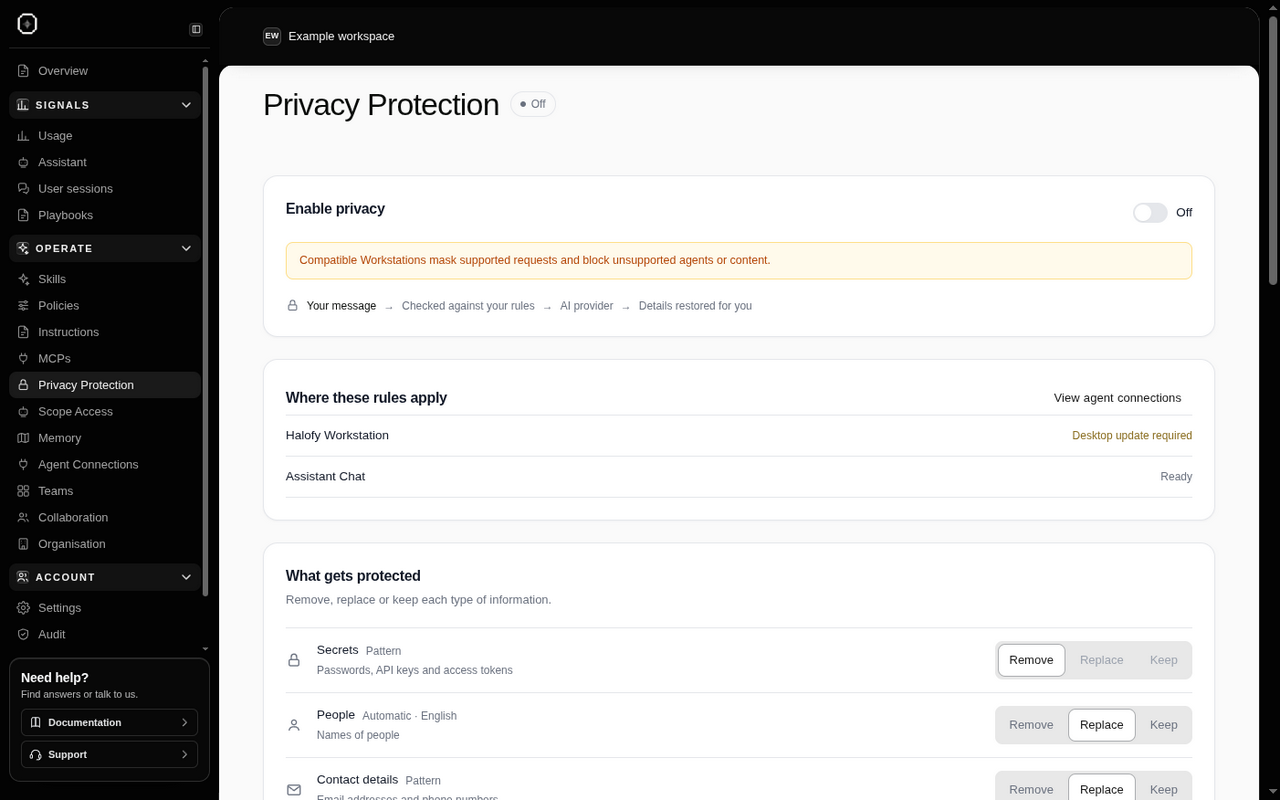
If your workspace requires Privacy Protection, Halofy applies its configured rules to supported text before sending it to the model. This can cover later requests containing conversation history and permitted tool results as well as your first message. Depending on the rule, a value is kept, replaced or removed.
Start a fresh conversation using a compatible local provider and sign-in method. Availability depends on the installed app, provider, operating system and requested tools. Attachments, reopening old conversations, switching models and some tools are unavailable in protected modes. Follow the compatibility message instead of assuming that normal provider access also supports protection.
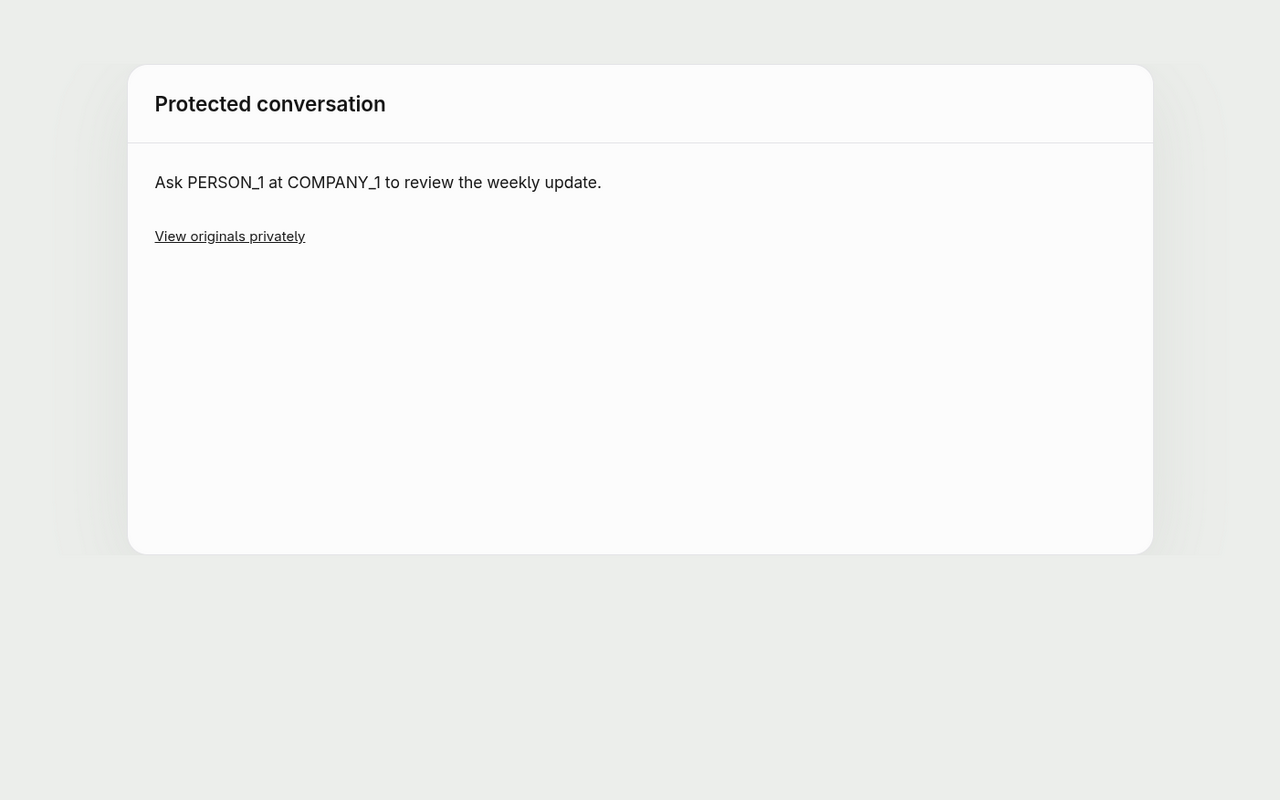
On web and desktop, a masked assistant response can offer View originals privately. Sign in separately as the person who started the conversation. Originals appear temporarily and clear when the view closes or authorization expires. Removed secrets cannot be restored.
Detection can miss unusual names, secrets or information outside the configured categories. Local tools can still read original files. Protection does not change access to the original user messages in the chat, recall a request already sent or enable protection on an incompatible host. If protection is enabled during ordinary work, stop that turn and begin a compatible protected conversation.
Understand what team device access shares#
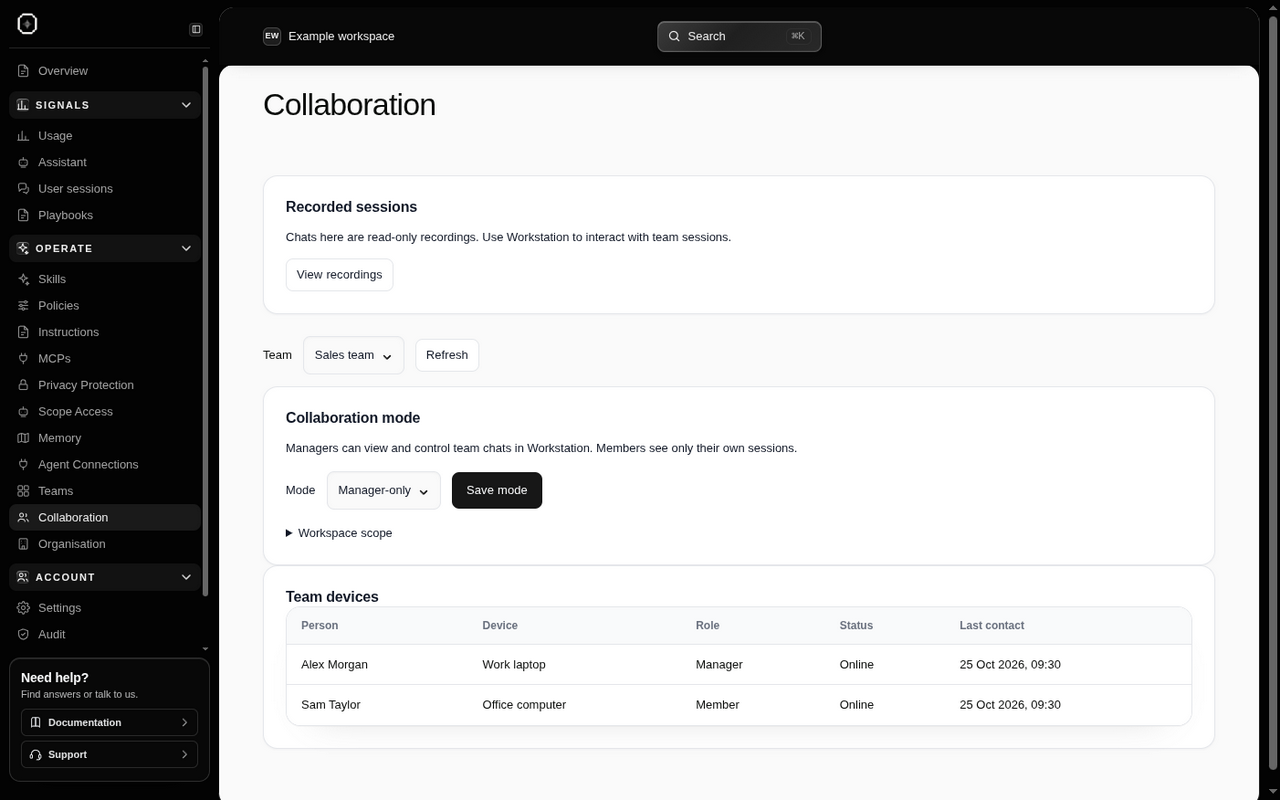
Live team collaboration and captured chat review are different permissions. In a control-enabled team mode, an authorized teammate can work with files and projects the host computer can reach, including folders outside the team’s projects. Existing personal chats stay separate; that does not make the rest of the computer private from someone with control.
The team grant does not let a teammate use the host owner’s Halofy account connection, discover their other account devices or manage plugin shares. Enable it only for the computers and people you intend to give this level of access.